Case study · Security

A 100 Gbit/s DDoS attack, beaten in 10 minutes

A ransom group gave our client 24 hours to pay 25 bitcoin or face a DDoS attack. Nobody paid. The next day the attack started, and this is how it was stopped.

Client
Gaming client (under NDA)
Service
Emergency IT support
Attack
UDP amplification
Mitigated in
10 minutes
Masked attackers — DDoS ransom threat

In numbers

25 BTC

ransom demanded

24 h

deadline given

~100 Gbit/s

attack traffic on the network

~120,000

infected nodes in the botnet

10 min

to beat the attack

01 — Challenge

One day a system administrator at our client received an extraordinary e-mail. A group calling itself “DD4BC” threatened to launch a powerful DDoS attack on the company’s site unless it paid, and gave it one day.

“Your sites are going under attack unless you pay 25 Bitcoin. […] We are giving you 24 hours to get it and pay us.”

Nobody replied, and nobody paid.

02 — Assessment

The next day the attack started, as promised. The attackers used the client’s IP addresses as targets for a UDP amplification attack against its uplinks.

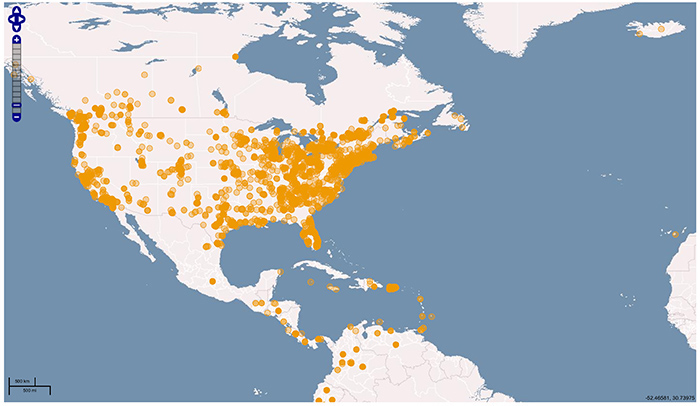
Comparing normal daily traffic with traffic during the attack, the network was taking roughly 100 Gbit/s of load. A traffic dump showed about 120,000 infected nodes producing it, a measure of how much firepower an average DDoS group has at hand.
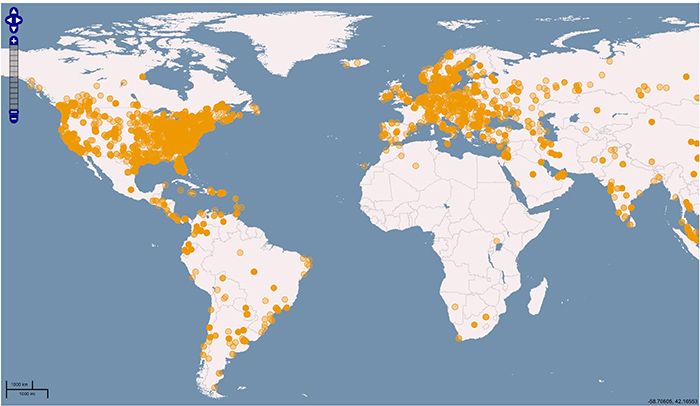
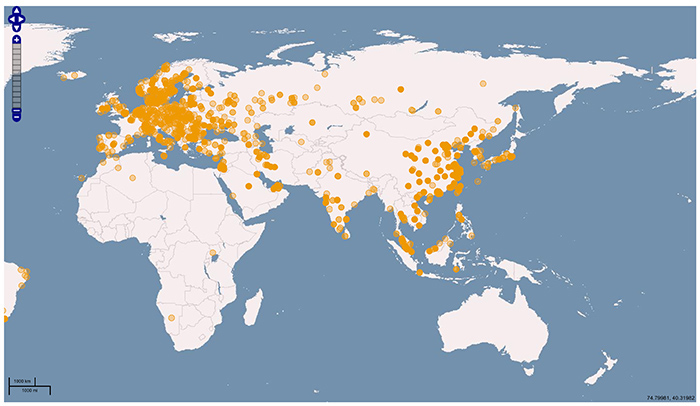
Map of hosts used in the UDP amplification DDoS attack (1 of 3)Map of hosts used in the UDP amplification DDoS attack (2 of 3)Map of hosts used in the UDP amplification DDoS attack (3 of 3)
03 — Response

Because the target was an IP address, we used BGP to send the attack traffic nowhere:

  1. Captured all traffic hitting the router uplinks during the attack.
  2. Applied BGP blackhole communities for the attacked IP addresses, so the traffic was discarded at the edge routers of the upstream Tier 1 ISPs.
  3. Brought the website up on other uplinks and routed it through Cloudflare to protect the infrastructure from the UDP flood.
04 — Result

The attack was beaten in 10 minutes. The site stayed online behind Cloudflare, no ransom was paid, and the client’s infrastructure was protected from further UDP floods.

Under attack right now?

Our TechOps team is available 24/7. Call us and we start immediately.